Post-quantum security analysis

Find quantum-vulnerable cryptography across your stack.

Rivet discovers cryptographic assets, scores quantum exposure, and maps findings to post-quantum replacements, so your team can plan migration from evidence.

Free 14-day trial · No credit card required
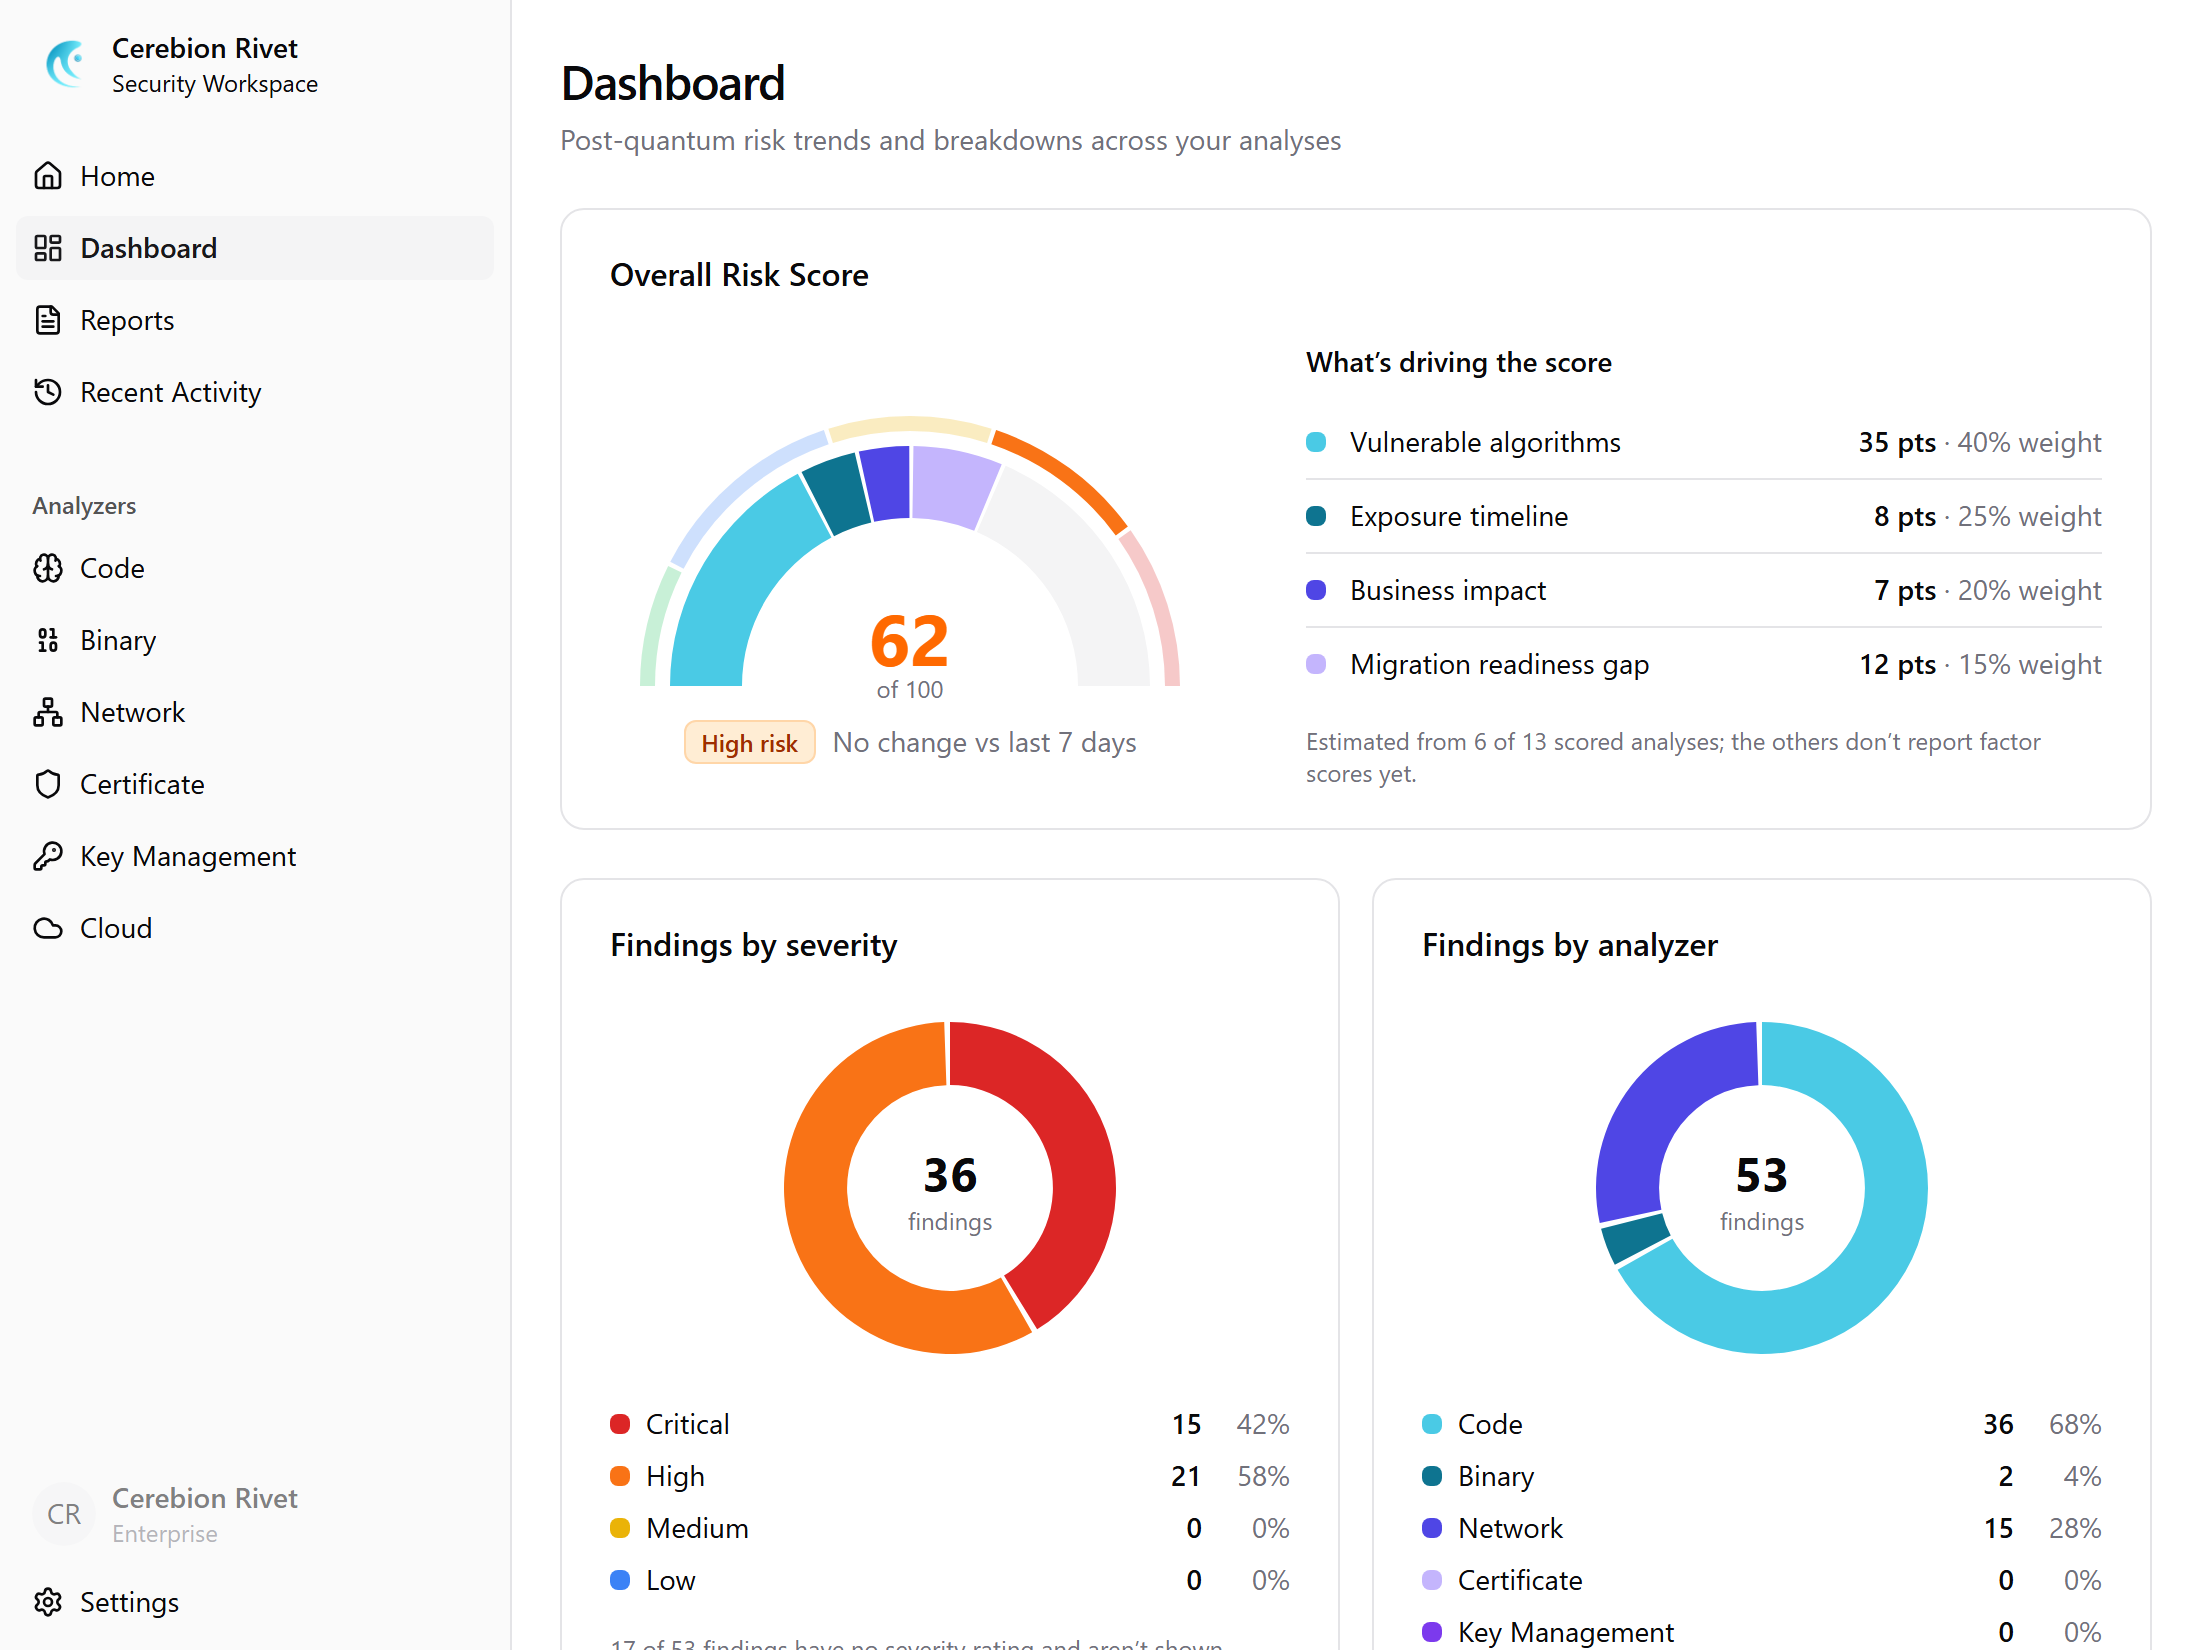
Rivet dashboard showing the overall risk score, PQC vulnerabilities, findings by severity and per-analyzer results

One platform

See cryptography across your environment.

Six analyzers bring the essential inventory into one risk view.

Code & binaries

Find cryptographic patterns in source code, compiled binaries, and configuration files.

Certificates & network

Check the digital certificates and secure connections that protect your websites, services, and data in transit.

Cloud & key management

Assess cloud services and key infrastructure across AWS, Azure, GCP, Vault, and more.

Code Analyzer

Advanced static analysis across 45+ languages and config file formats.
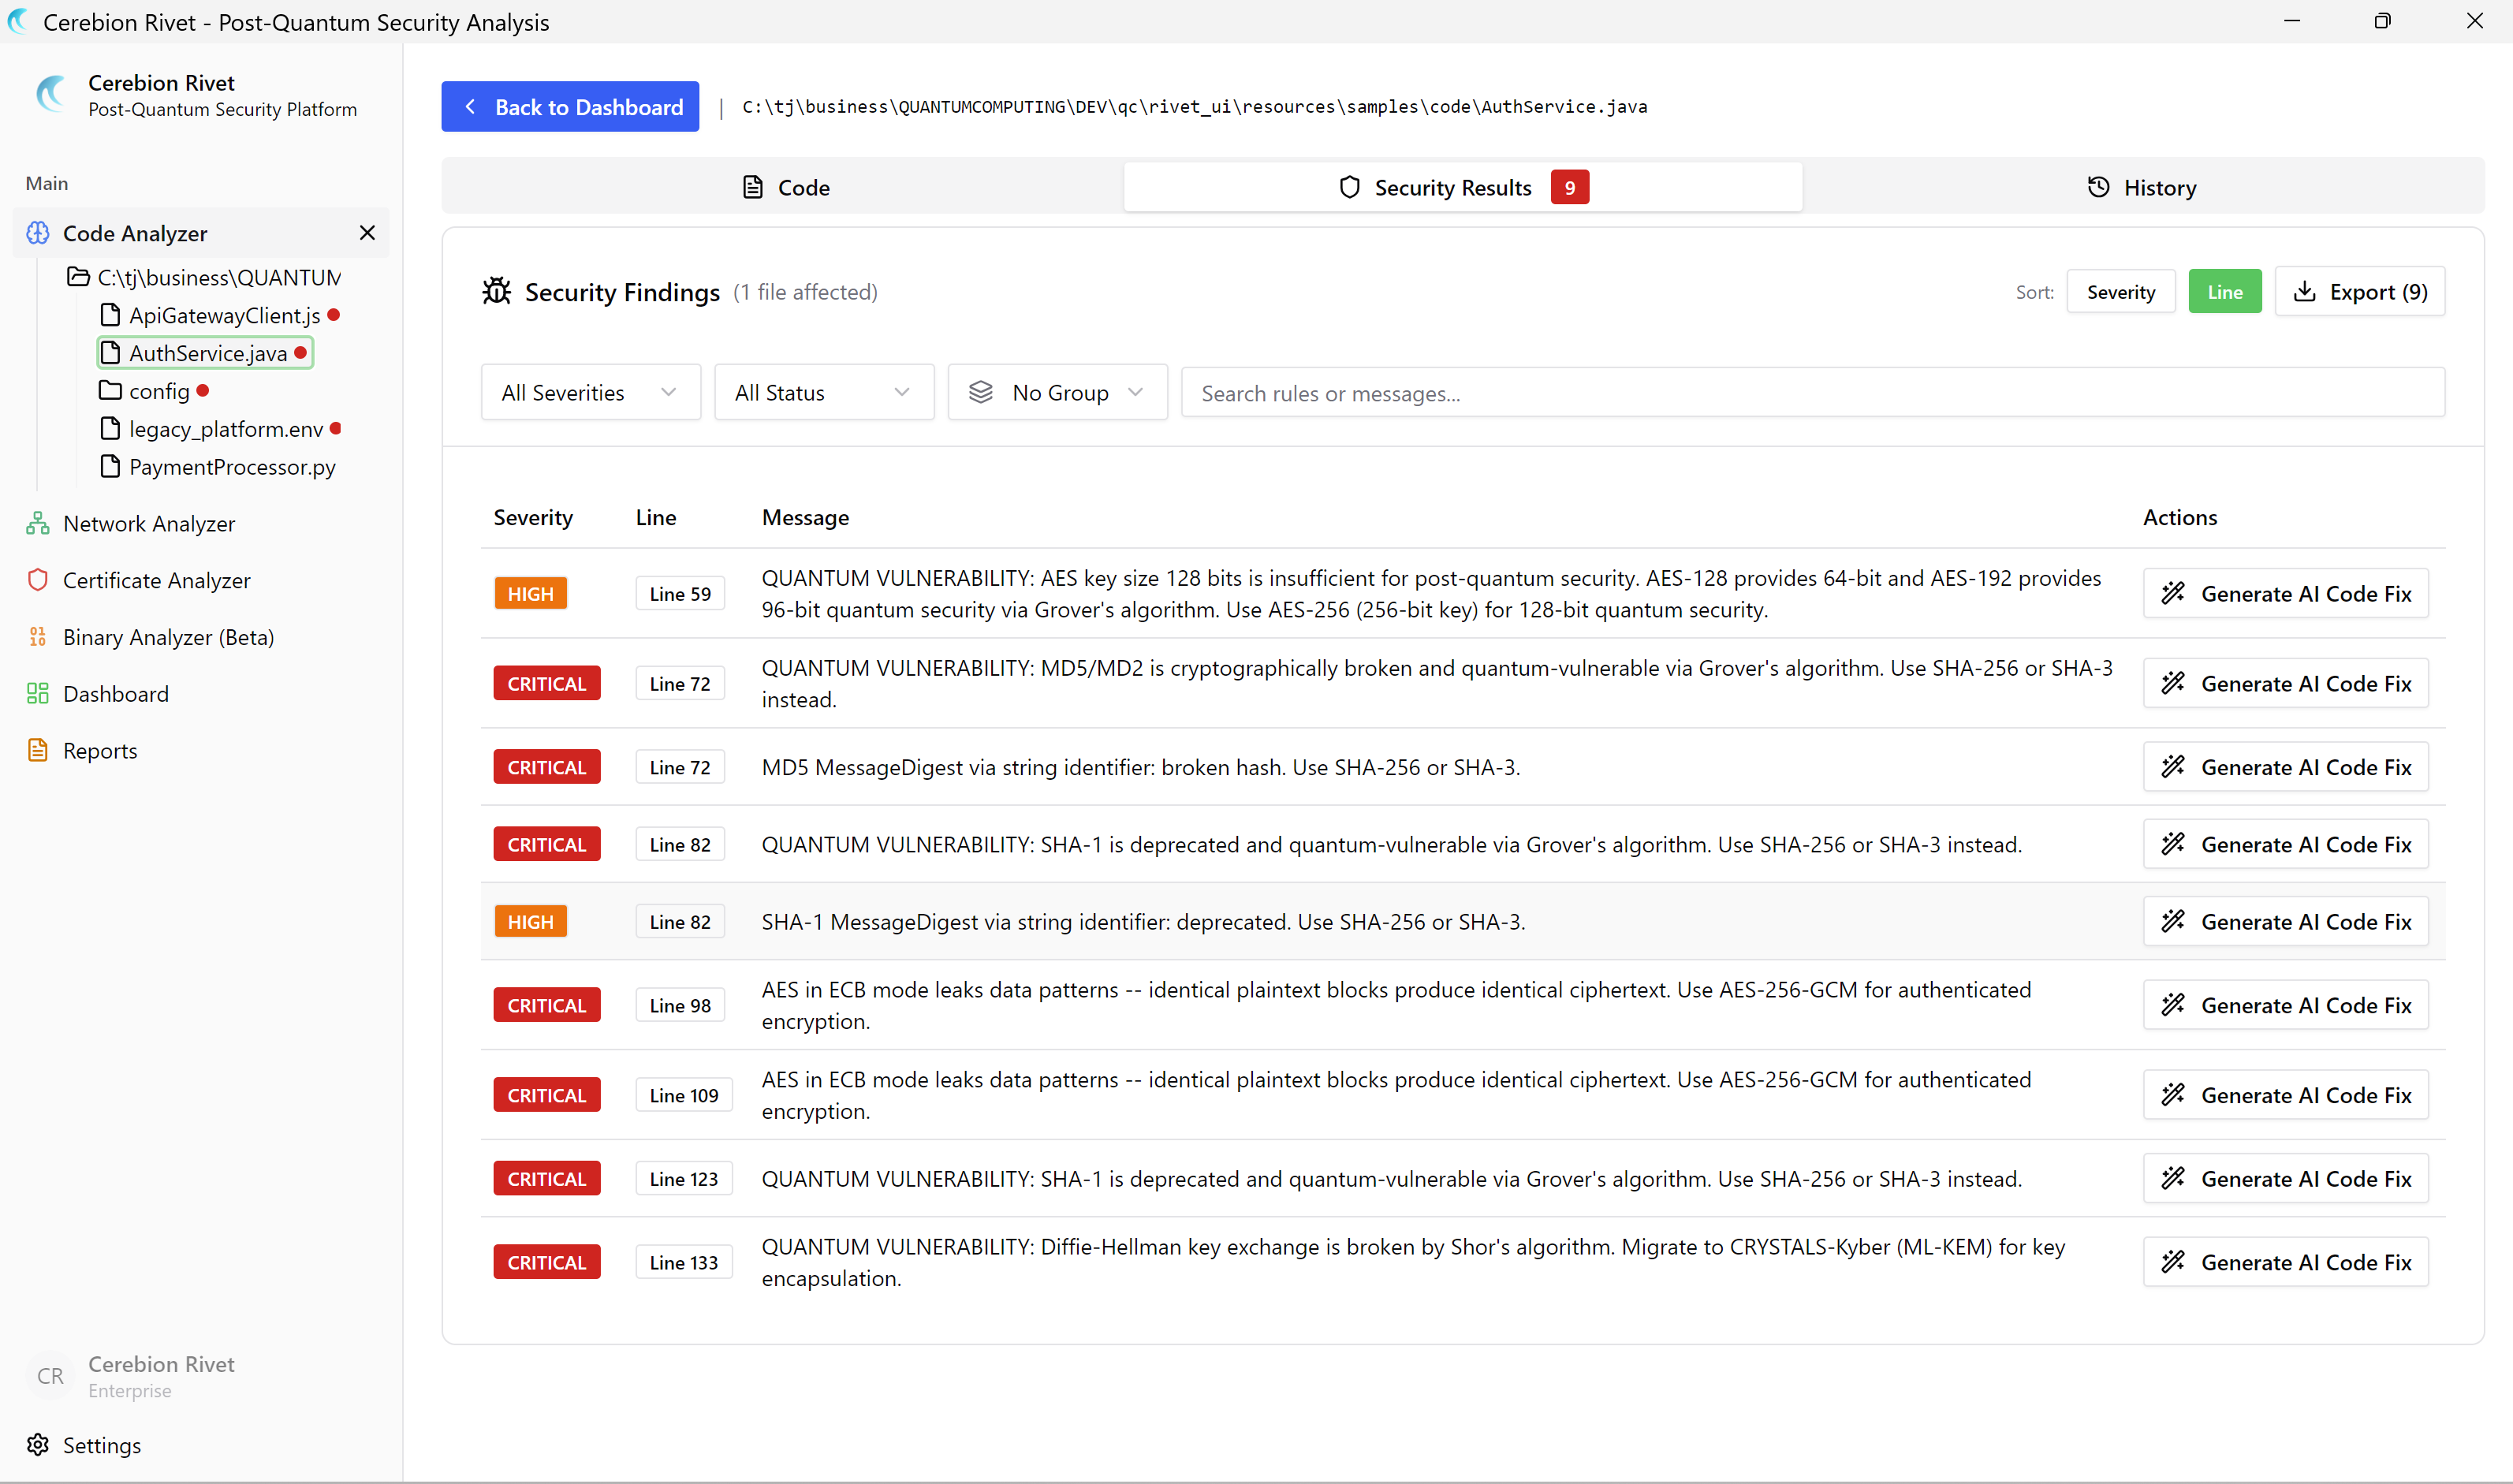
  • 45+ languages and file types including Python, Java, C#, Go, Rust, C/C++
  • Custom PQC-specific detection rules
  • Rule-based and AI-assisted fix recommendations
Code Analyzer screenshot

Binary Analyzer

beta

Analyze compiled binaries (EXE, DLL, ELF, Mach-O) for quantum-vulnerable cryptographic patterns.
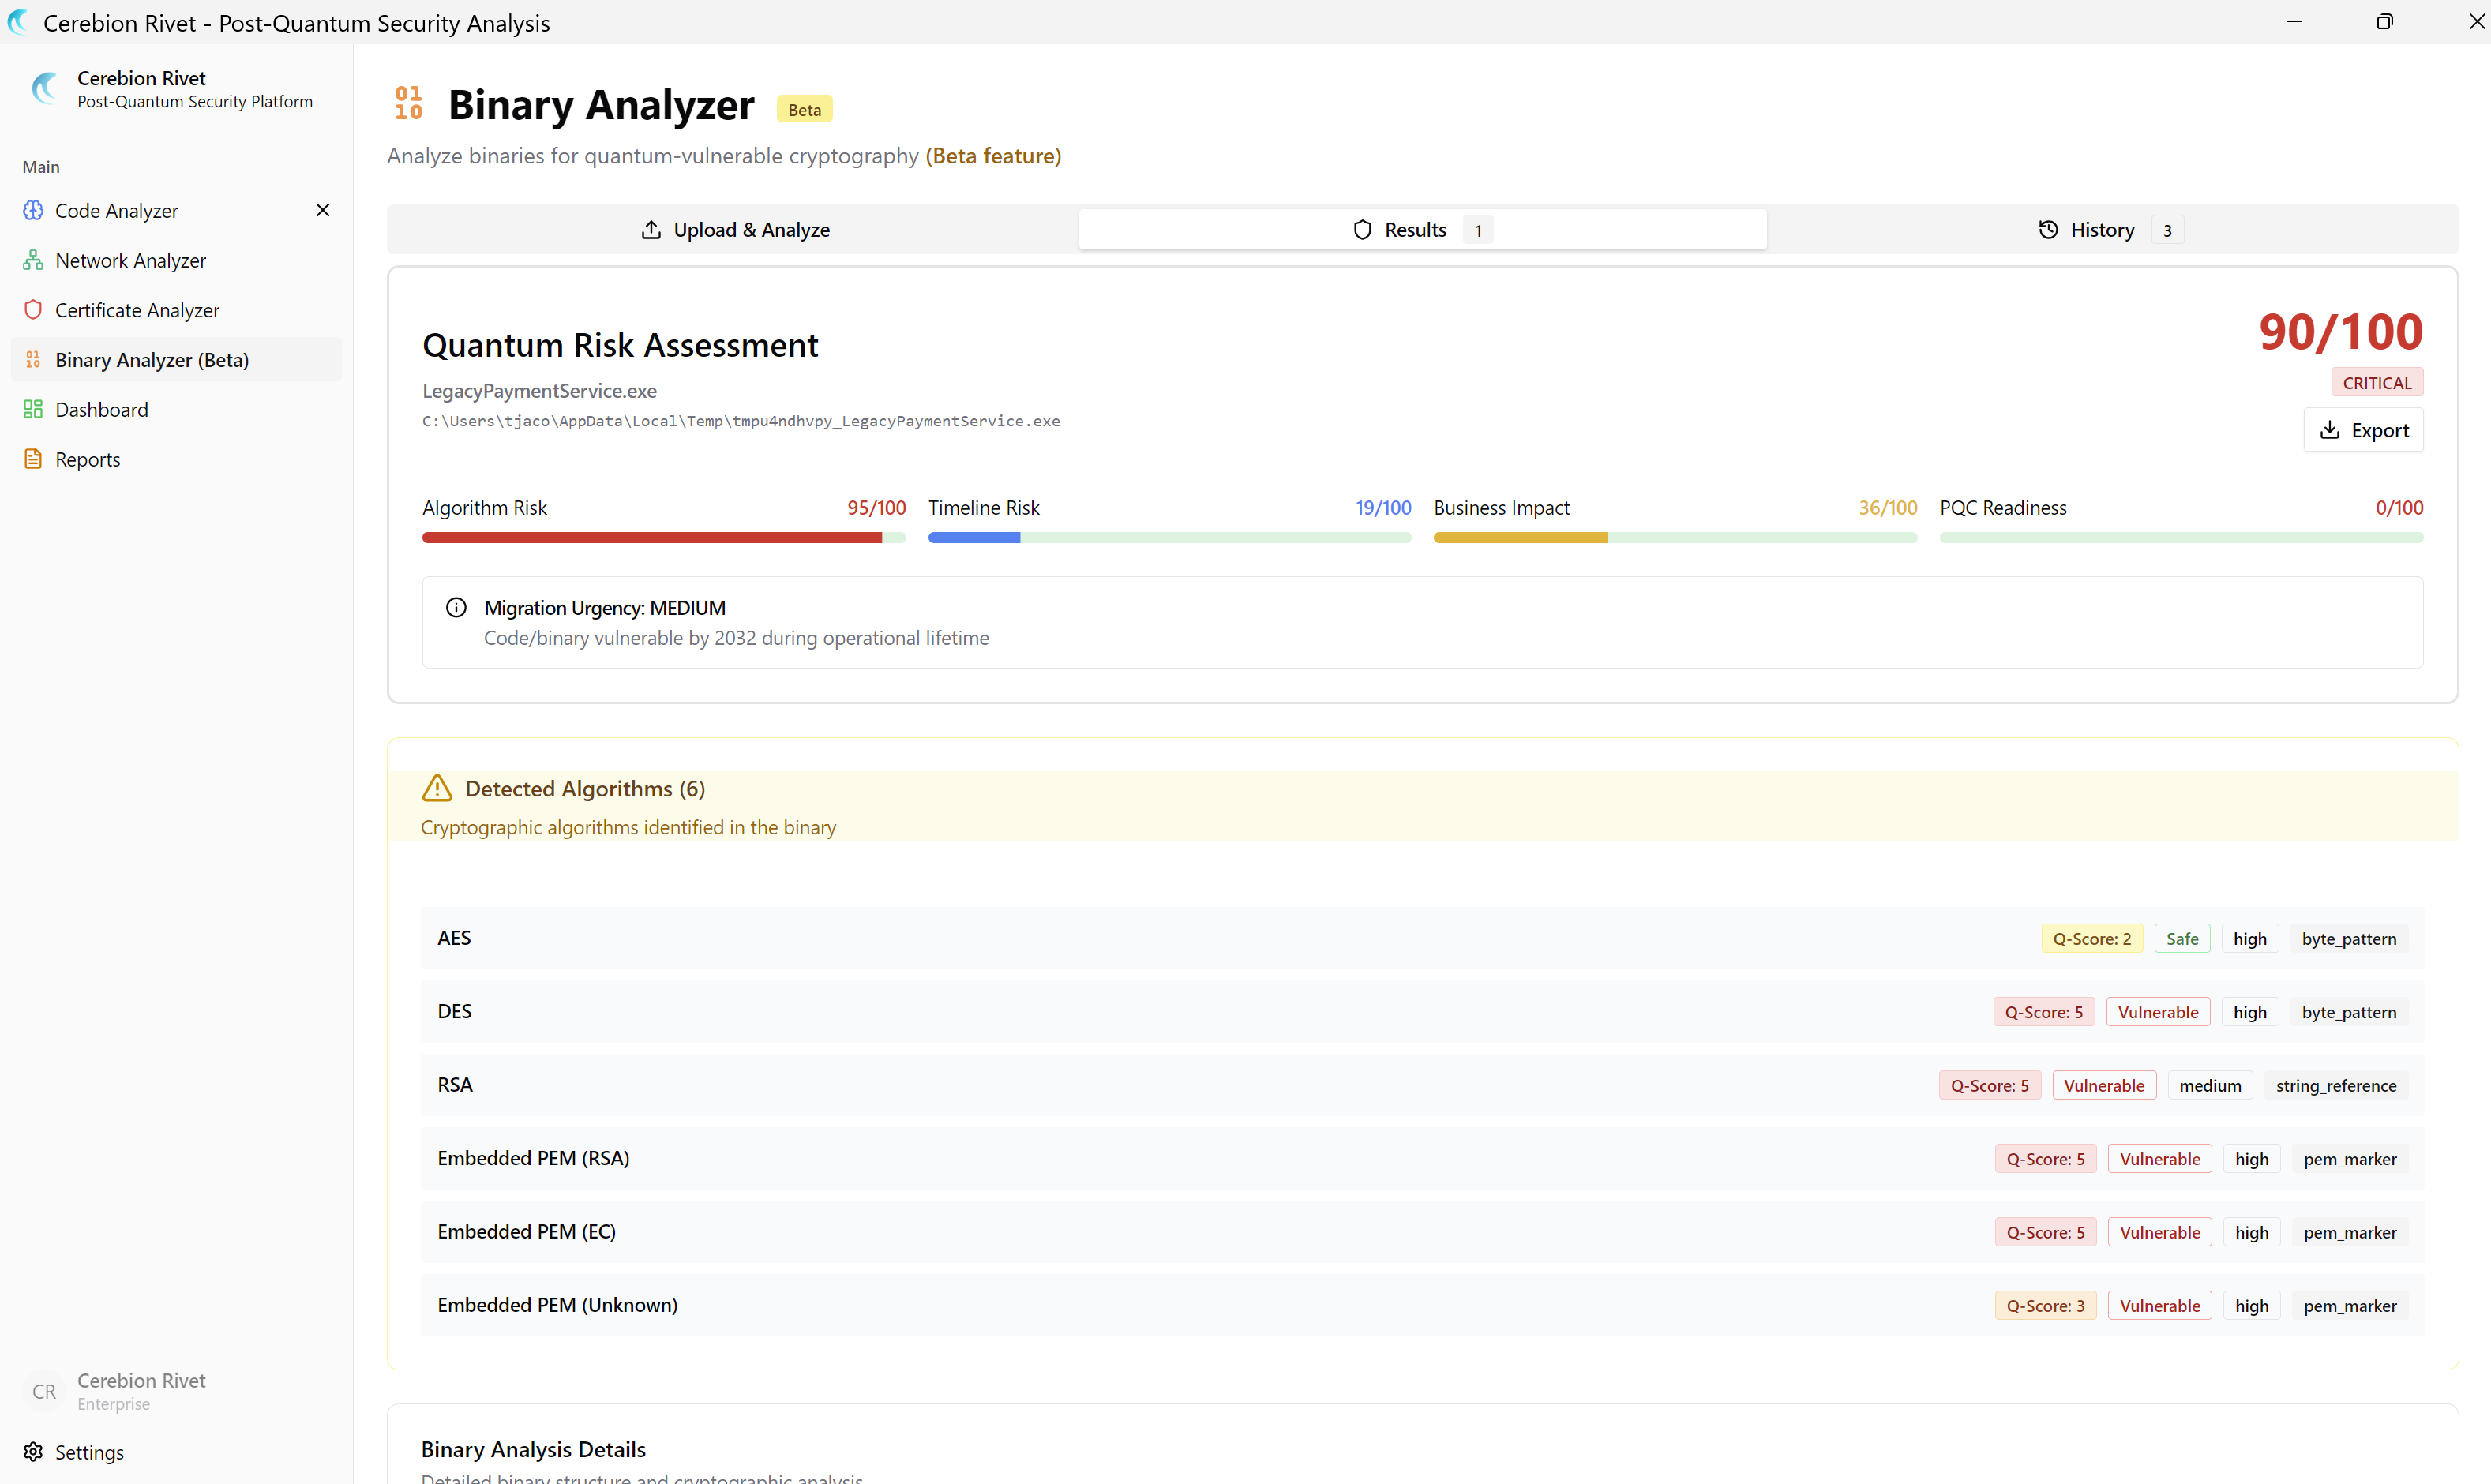
  • Cross-platform binary parsing across PE, ELF, and Mach-O formats
  • Quantum-specific pattern detection with Q-Score severity ratings (1-5)
  • Analyze Windows, Linux, and macOS binaries from any OS
Binary Analyzer screenshot

Certificate Analyzer

Assess certificates, TLS key exchange, and identity provider signing keys for algorithms that quantum computers will break.
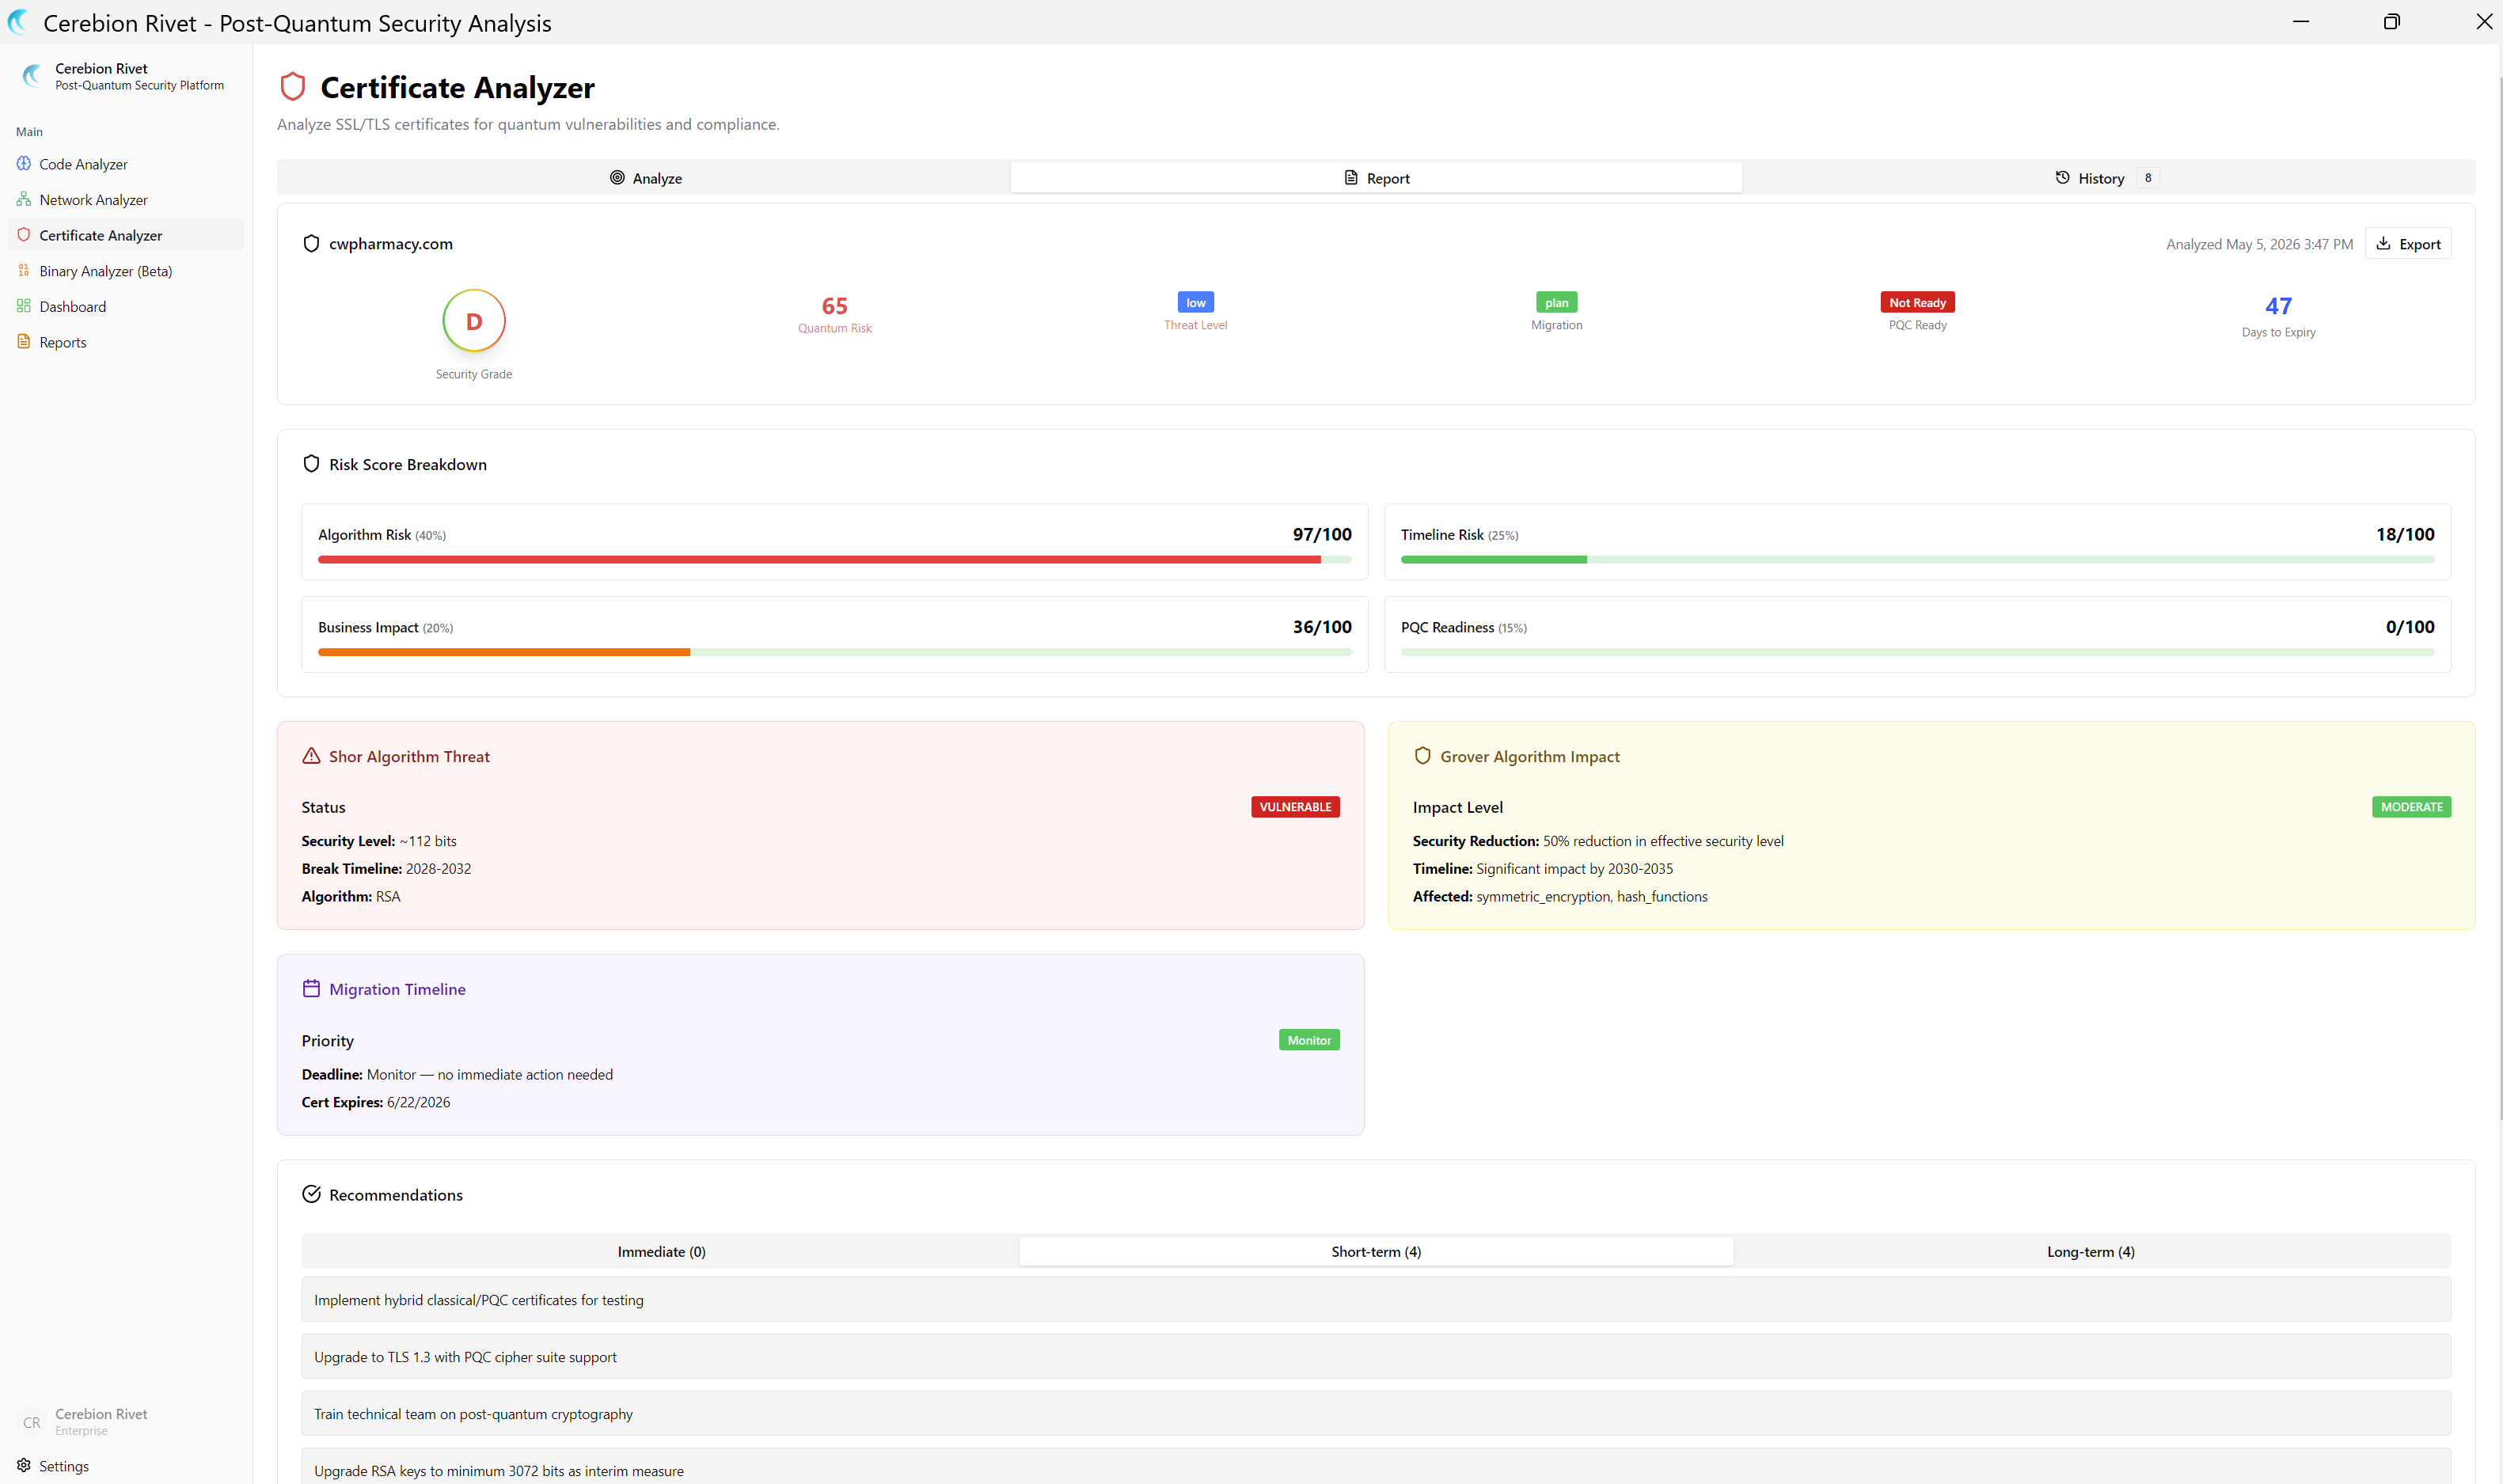
  • RSA, ECC, and DSA quantum vulnerability assessment
  • Live domain scanning with quantum risk scoring
  • Identity provider (SSO) signing key analysis for OIDC, JWKS, and SAML
  • Hybrid post-quantum key exchange detection
  • PEM and DER certificate file upload support
Certificate Analyzer screenshot

Network Analyzer

Analyze live hosts and network configurations for quantum-vulnerable TLS and cipher suites.
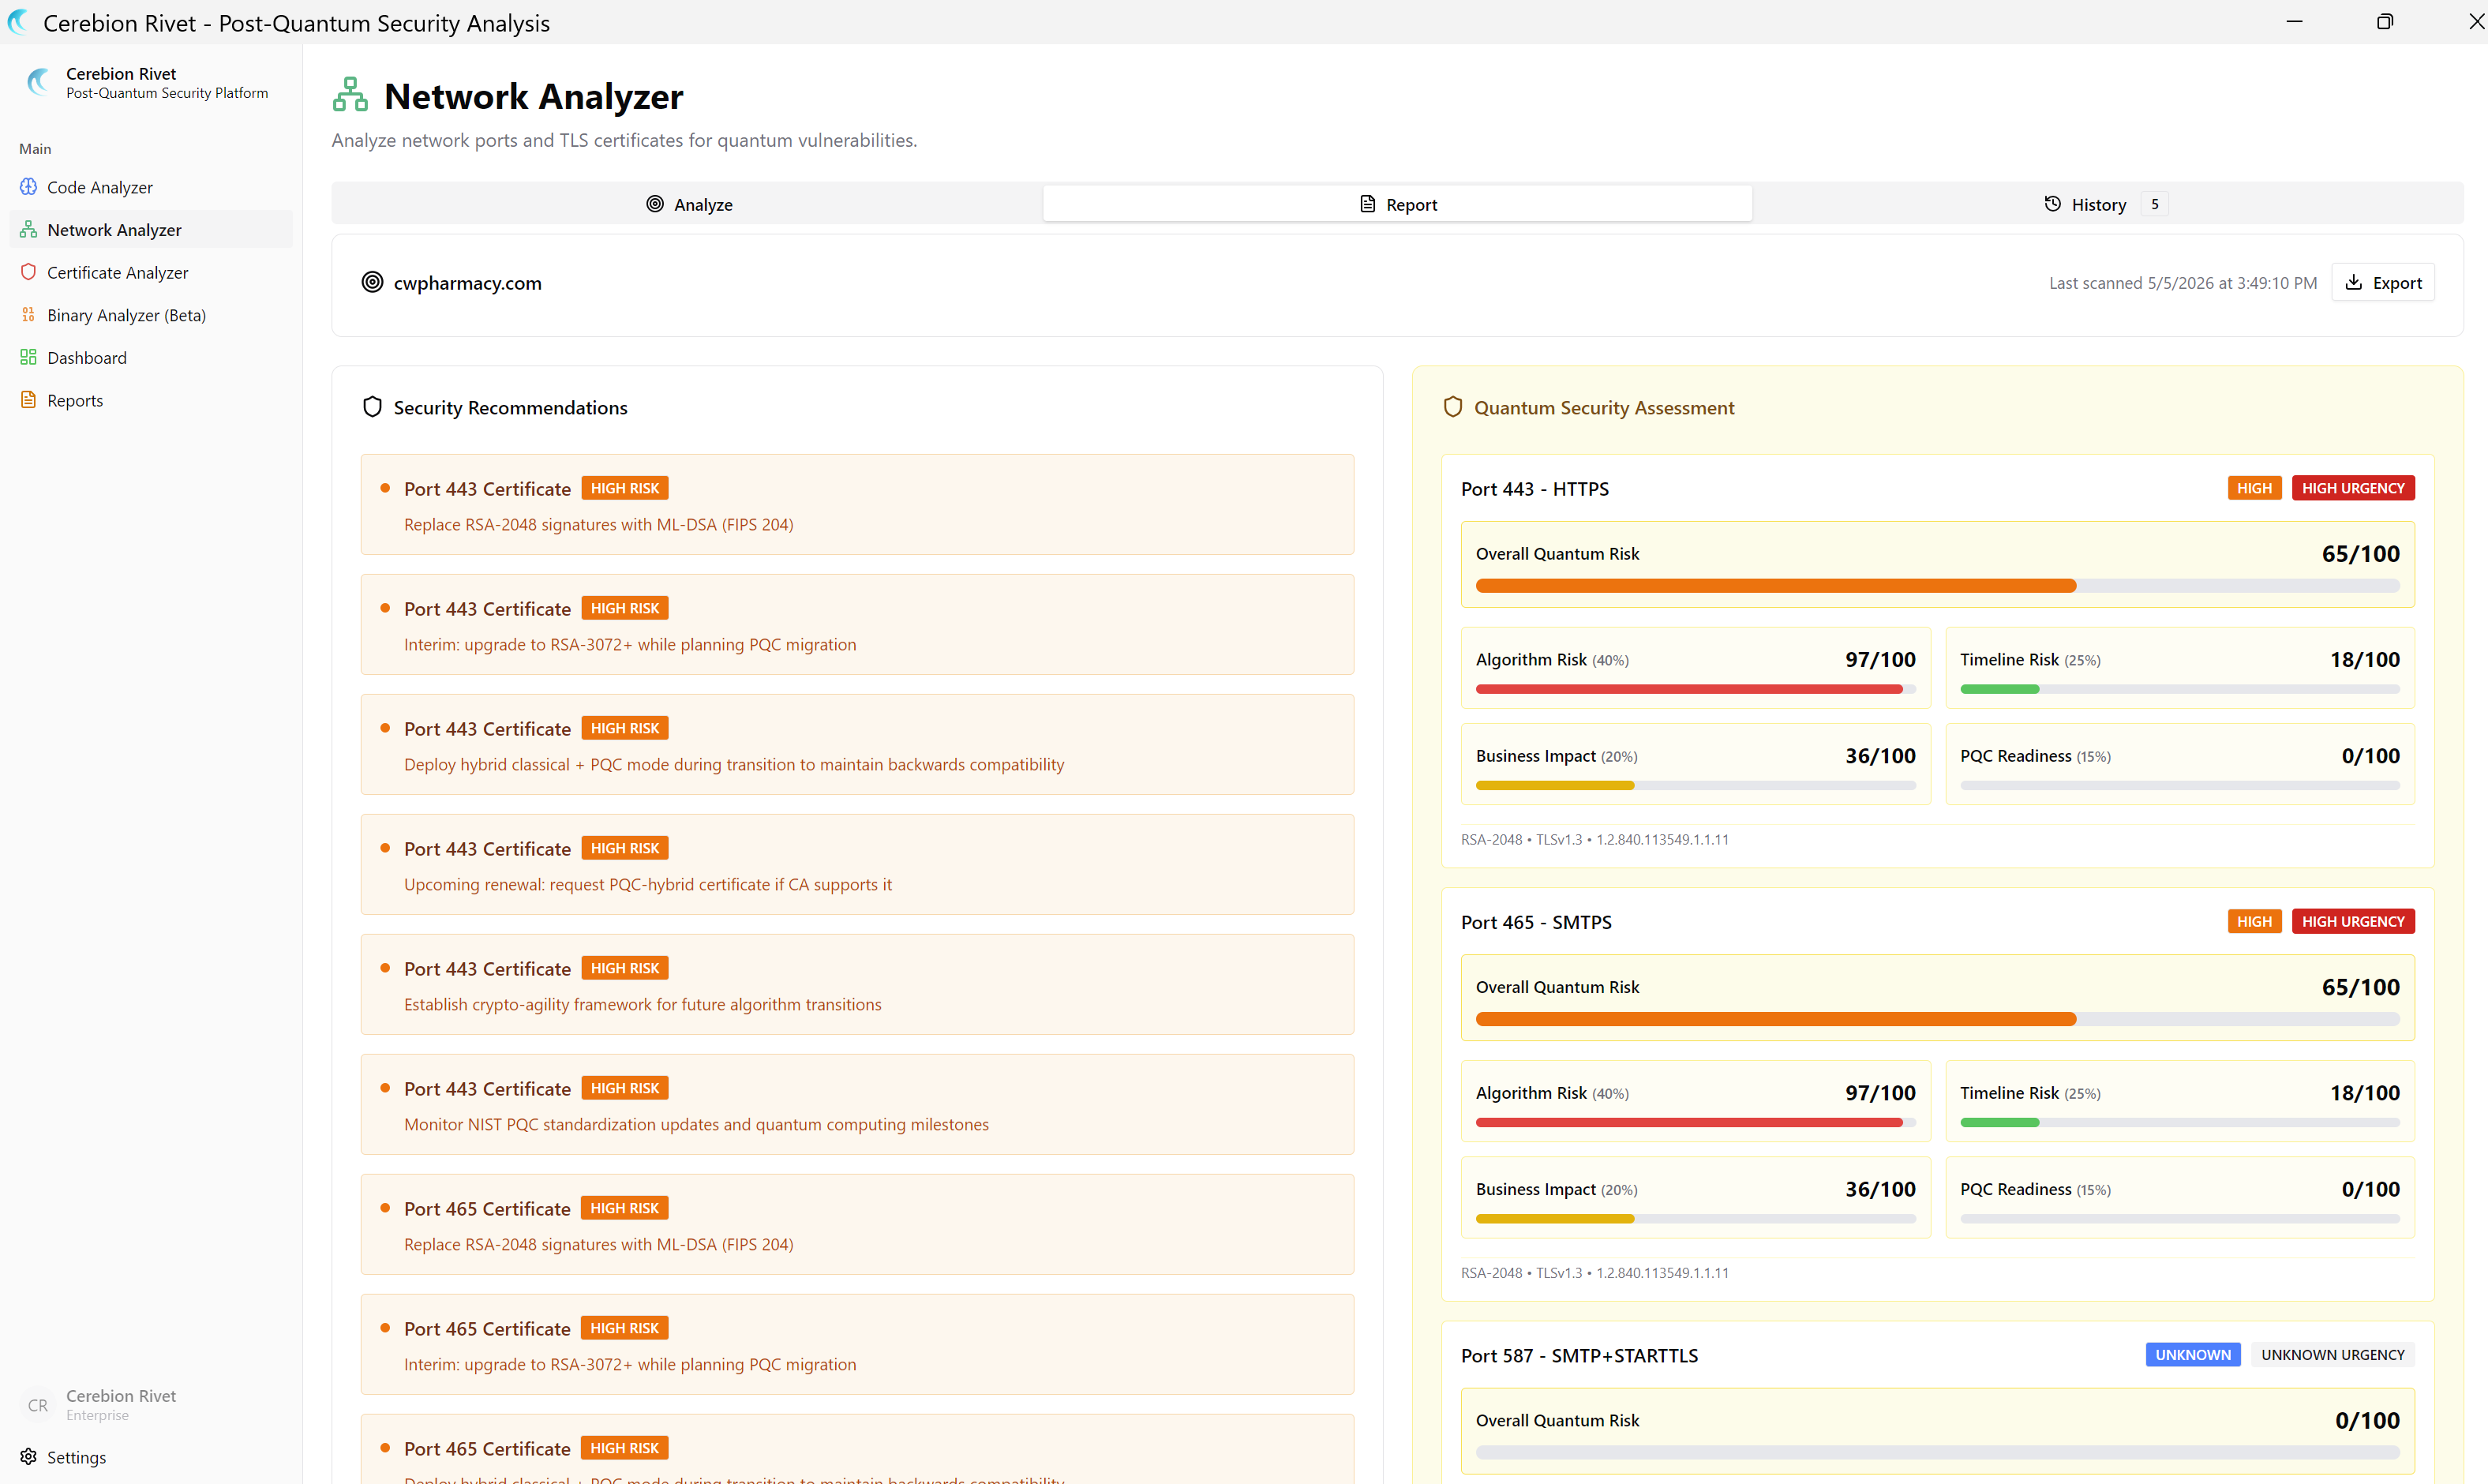
  • TLS version and cipher suite analysis
  • TLS and SSH key exchange, including post-quantum
  • Mail, database, and directory servers that upgrade to TLS
  • Certificate chain validation
  • Bulk host scanning
Network Analyzer screenshot

Cloud Analyzer

Scan live cloud infrastructure for quantum-vulnerable cryptography across AWS, Azure, and GCP.
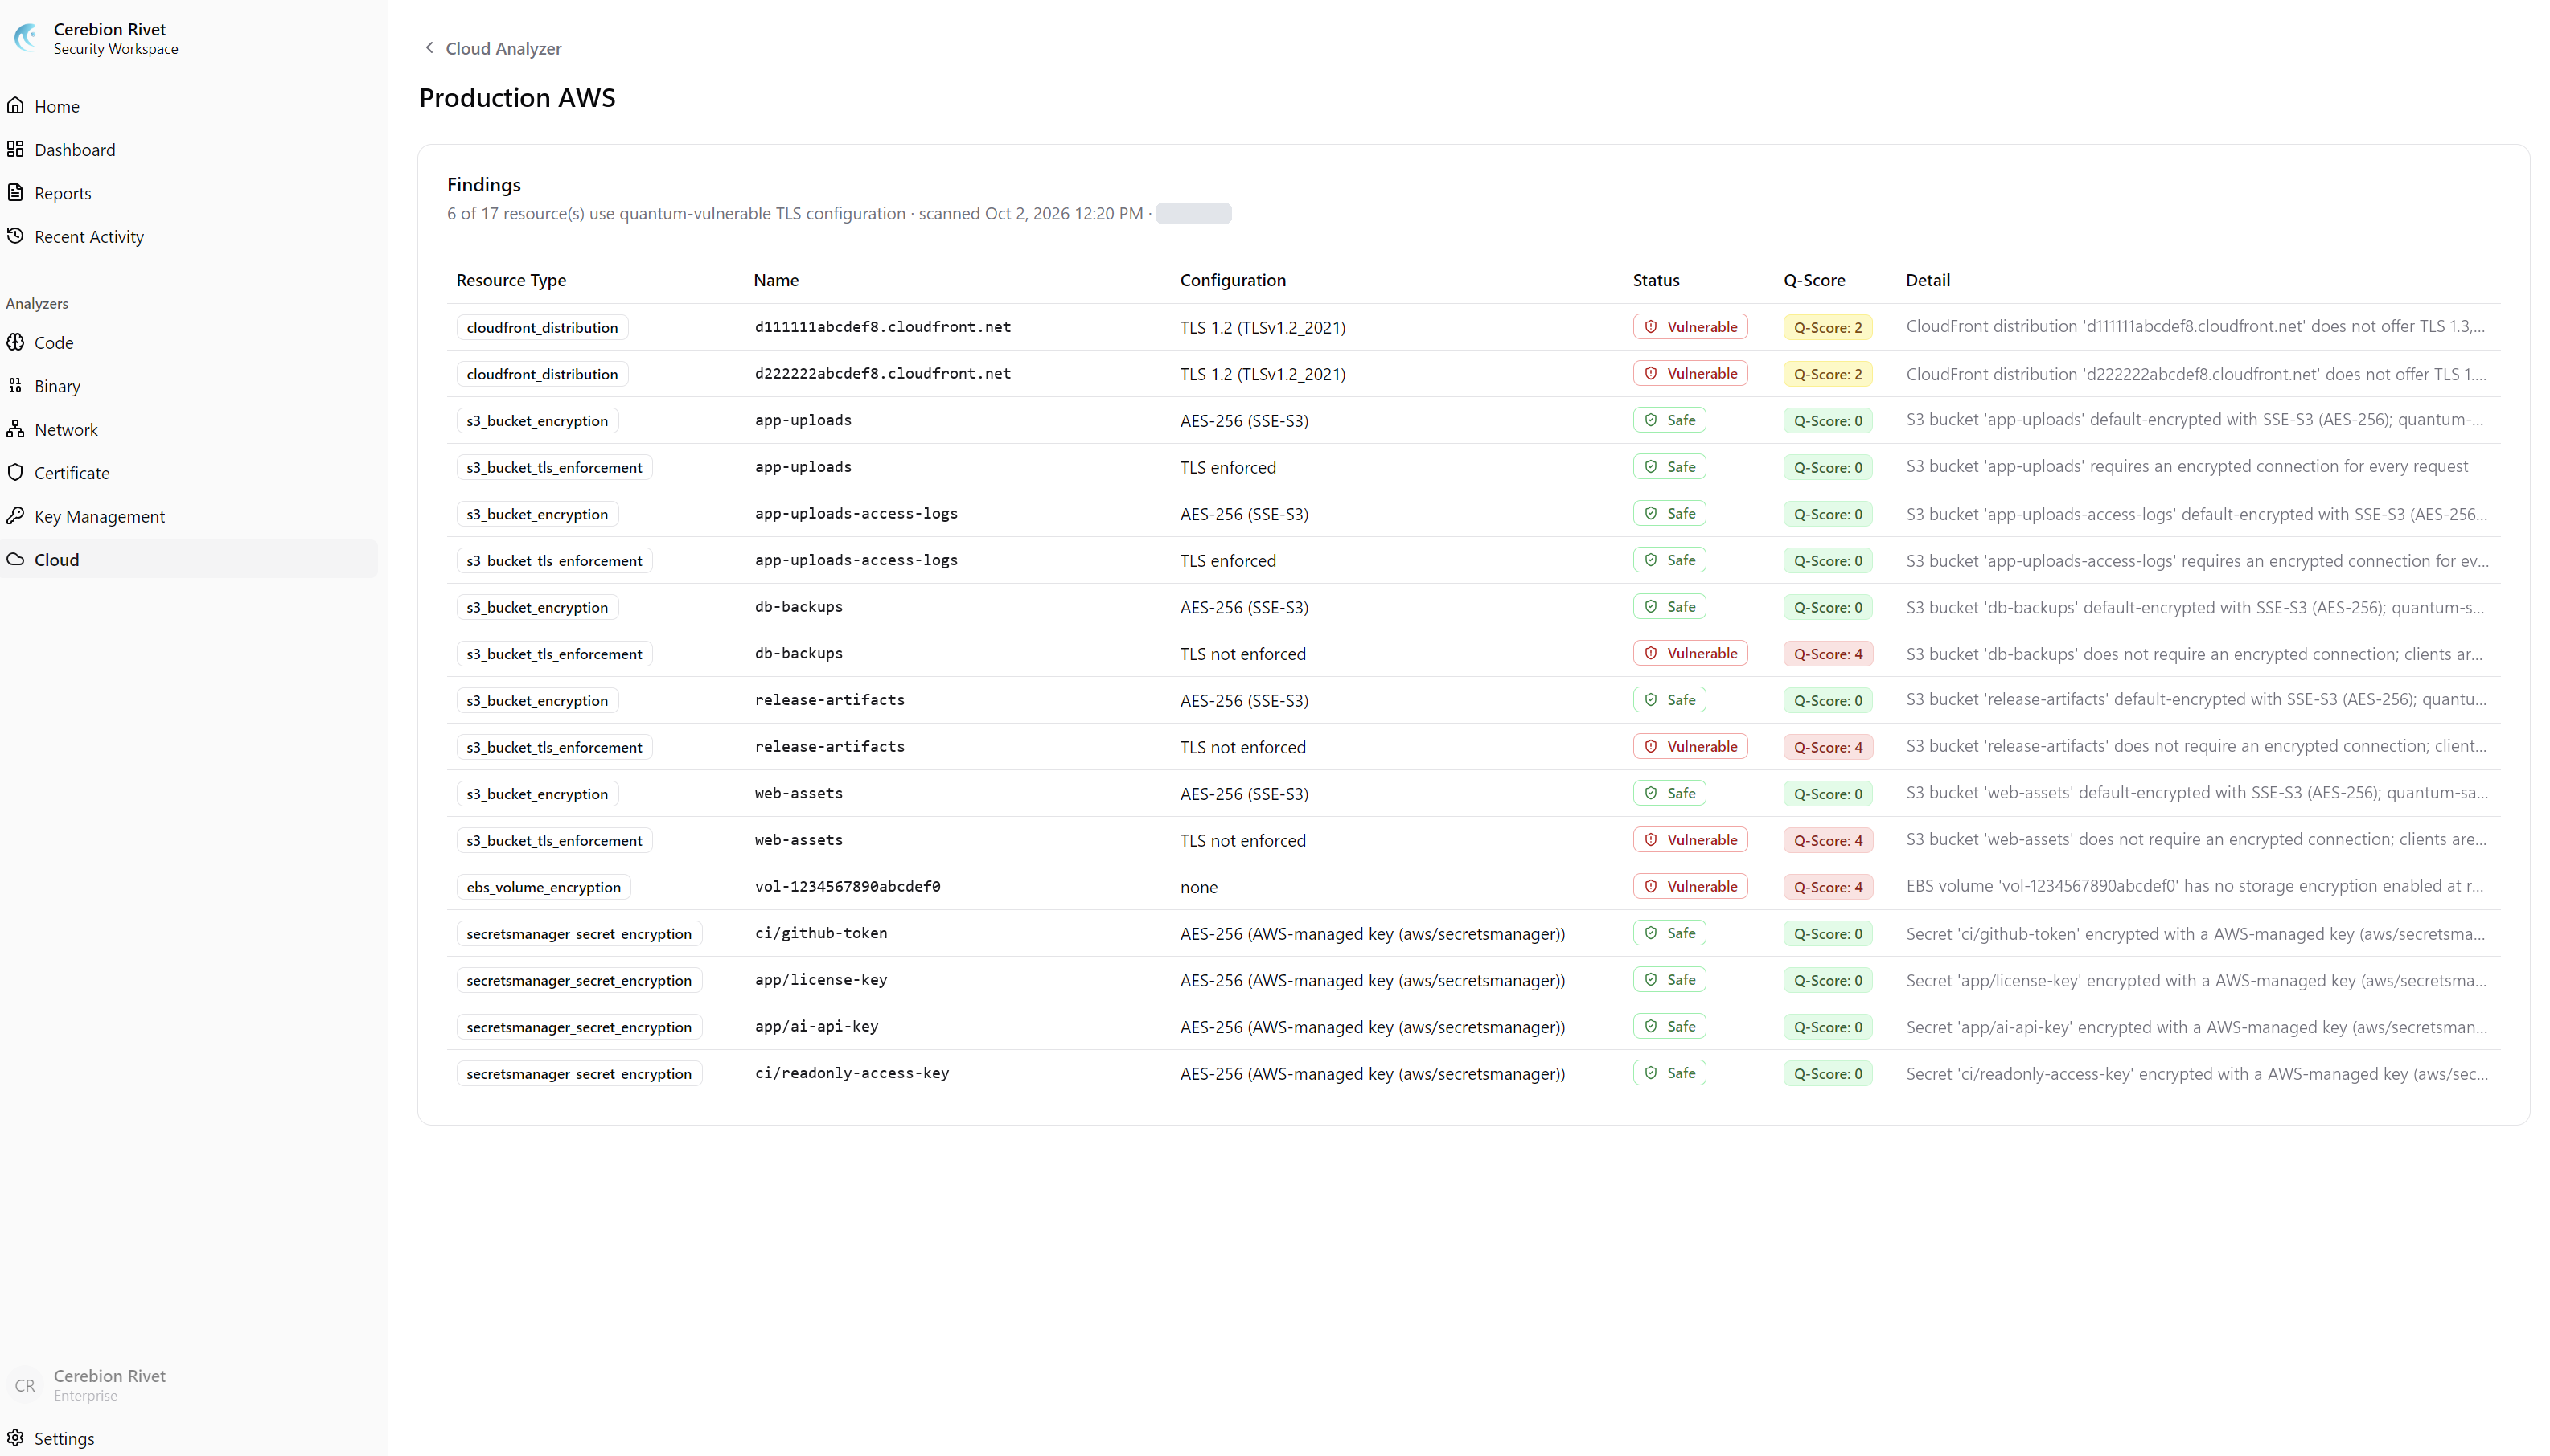
  • AWS: load balancers, CloudFront, API Gateway, S3, RDS, EBS, Secrets Manager, CloudHSM
  • Azure: Application Gateway, Storage Accounts, SQL Server
  • GCP: load balancer SSL policies (including post-quantum key exchange), Cloud Storage, Cloud SQL, Secret Manager
Cloud Analyzer screenshot

Key Management Analyzer

Scan live key and certificate infrastructure across HashiCorp Vault, AWS, Azure, GCP, Kubernetes, and Microsoft AD CS for quantum-vulnerable algorithms.
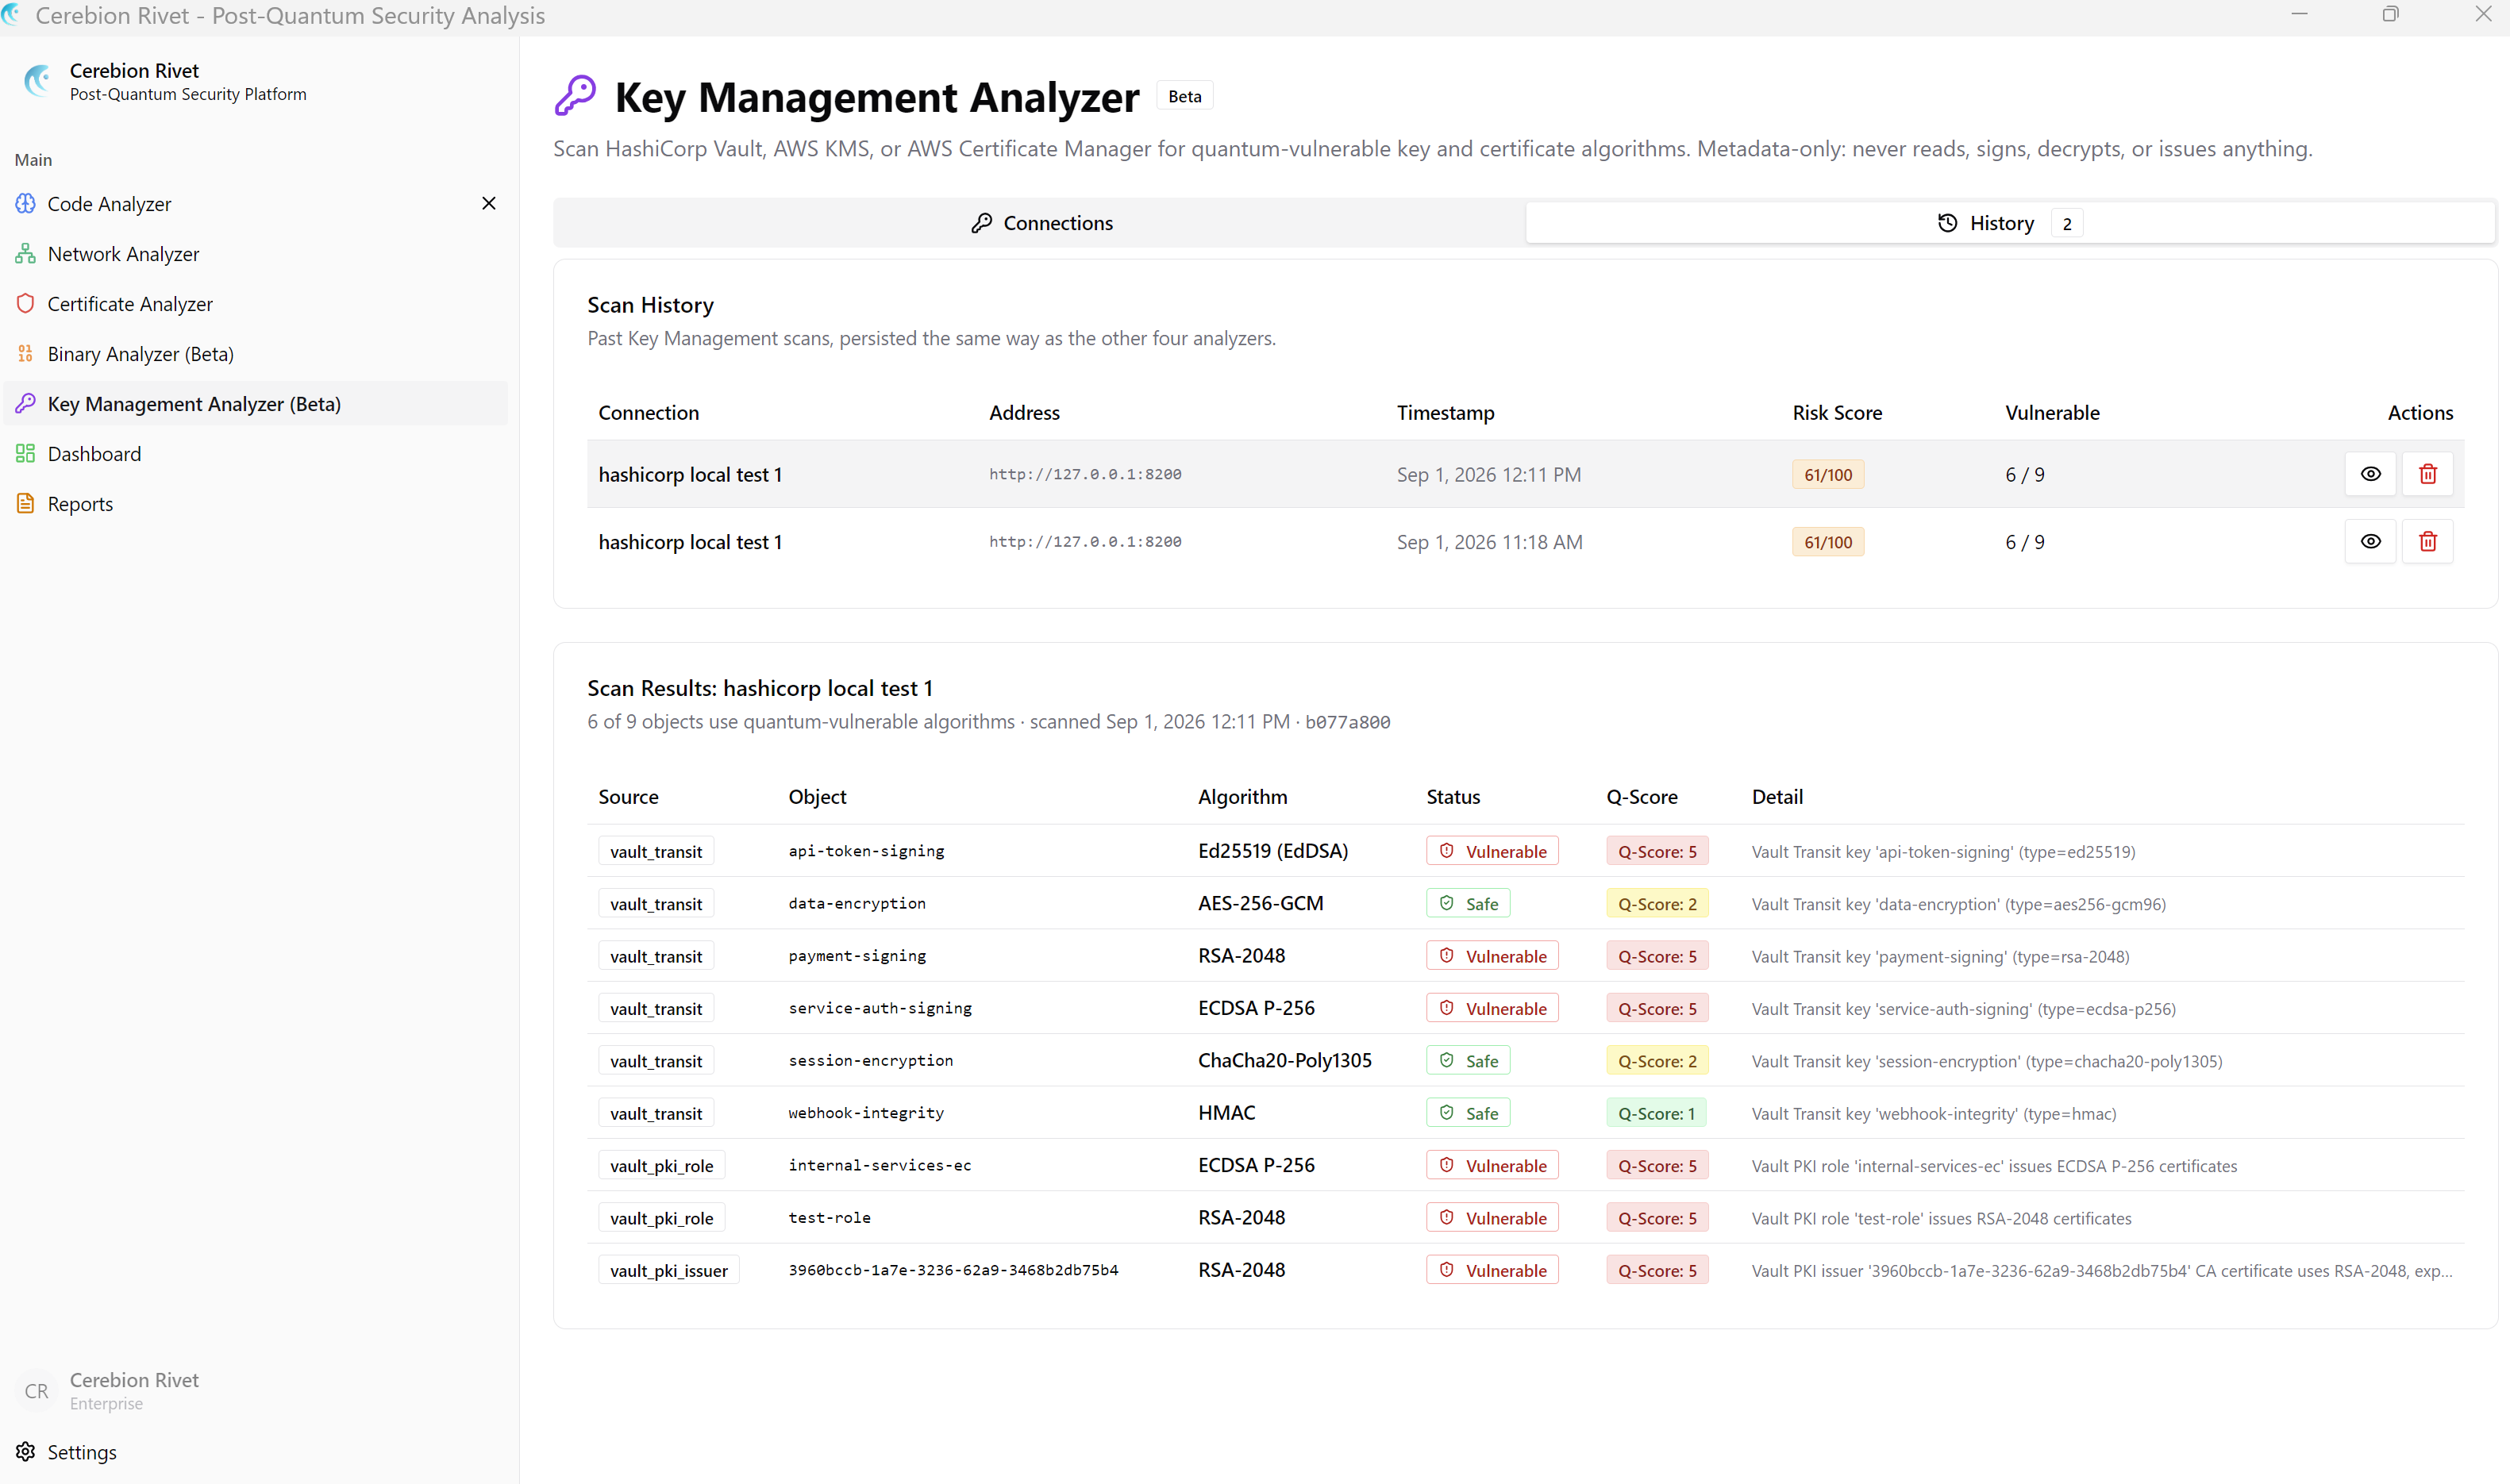
  • 8 backends: Vault, AWS KMS/Certificate Manager, Azure Key Vault/Managed HSM, GCP Cloud KMS, Kubernetes Certificate Manager, and Microsoft AD CS
  • Metadata-only, by design: the connector interface has no decrypt, sign, or export capability
  • Uses your own scoped, read-only credentials
Key Management Analyzer screenshot

Swipe to see all six analyzers

A clear process

From discovery to remediation.

Move from scattered findings to a focused migration plan.

  1. 1

    Discover

    • Code and binaries
    • Certificates and TLS endpoints
    • Cloud and key management systems

    Cryptographic inventory

  2. 2

    Assess

    • Quantum-vulnerable algorithms
    • Usage patterns
    • Technical context

    Vulnerability context

  3. 3

    Prioritize

    • Contextual quantum risk score
    • Exposures ranked by risk

    0–100 risk score

  4. 4

    Remediate

    • NIST post-quantum alternatives
    • Rule-based guidance
    • Optional AI-assisted fixes

    NIST migration path

Built for enterprise

Your environment. Your controls.

Run scans where your teams work, on infrastructure you control, and decide how AI-assisted guidance is used.

  • Desktop, server or pipeline

    Run Rivet on desktops, laptops, servers or in CI/CD pipelines, all on infrastructure you control.

  • Air-gapped support

    Core scanning works in isolated environments.

  • CLI and automation

    Script scans with the command line, export SARIF and JSON, and connect AI tools through MCP.

  • Flexible AI

    AI is optional; rule-based guidance needs no API key.

Start with your cryptographic inventory

See what is in your environment.

Start a free 14-day trial. No credit card required.